


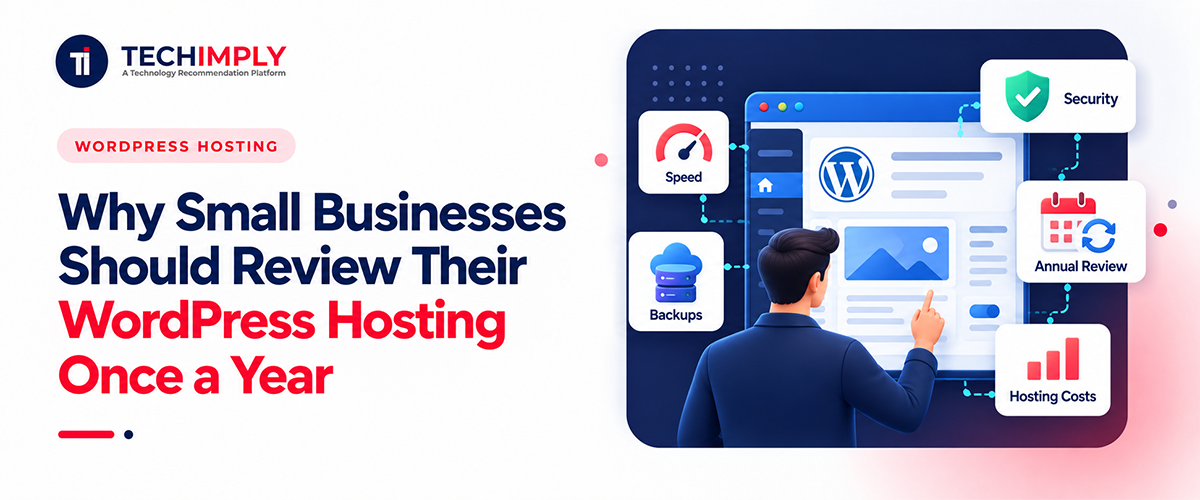
A website can change substantially during twelve months. New extensions are installed, traffic increases, staff accounts accumulate, storage expands, and business processes become dependent on forms or online sales. The original technical decision may no longer match the site's workload or the company's tolerance for interruption.
An annual review creates a scheduled point for checking capacity and recovery alongside security and cost. Administrative control receives its own examination. The review complements regular maintenance and urgent security work while recording changes that require action during the next year.
Business Dependence and Ownership
Begin with the role the website now performs. Owners can identify revenue functions and customer-information collection, then add staff support and contractual obligations. Each function needs a named contact and a defined period of tolerable unavailability.
Account ownership also deserves attention. Confirm organizational control of domain registration and billing, along with administrative credentials and recovery contacts. Remove access held by former employees and contractors. Verify renewal dates and payment methods before an expired card or inaccessible email address causes an avoidable interruption.
Steps to evaluate and improve website security include updates, strong account controls, encrypted connections, software cleanup, and backups. An annual review can use this practical structure while identifying important assets, current protections, responsible people, and prioritized improvements.
Capacity and Performance Evidence
Compare current traffic with the previous review period. Peak concurrent visits and server response time expose short periods of pressure.
Storage growth, database size, transfer use, error rates, and resource ceilings reached during promotions add the technical context. Average monthly traffic can conceal brief customer-facing delays.
Follow important user routes on mobile and desktop connections. Test the homepage and key landing pages before moving through search, forms, account access, and checkout where applicable. Slow database calls, large images, unused scripts, and excessive extensions can then be assigned for correction.
The coming year's plans belong in the assessment. A catalogue expansion, membership feature, advertising increase, or entry into a new region may change resource and support requirements. Capacity decisions are more useful when tied to a documented event and estimated load.
Backup Restoration
Examine backups at the file and database levels, then follow a complete business process after restoration.
Confirm the schedule, retention period, storage location, encryption, and content included. A site that now holds customer uploads or transactional records may require a different schedule from the one chosen at launch.
Computer Weekly's explanation of backup testing emphasizes that recovery must be tested and documented. Restore a recent copy in an isolated location and confirm that the site opens. Exercise essential functions, then record restoration time and any missing dependency.
Define how much data the business can lose and how quickly critical service must return. These targets determine if the current backup frequency and restoration process remain suitable. Credentials, contact information, and step-by-step instructions also need updating after staffing or technical changes.
Software and Security Condition
Inventory the core system and theme, then add extensions, custom code, and connected services. Unsupported or abandoned components require replacement planning. Remove unused extensions because deactivation alone can leave code and data present.
The security assessment covers update practices and administrator accounts. Multifactor authentication, file permissions, encrypted connections, logging, and recent suspicious activity require separate review. What pentesting is includes simulated attacks used to identify practical weaknesses in an application or network. A small business can select tests according to its risk and technical complexity.
Automated scanning can assist, but findings need review by a qualified person. False positives can waste effort, while business-logic weaknesses may require manual examination. Give any test that could affect service or data a defined scope, authorization, monitoring, and recovery precautions.
Account Access Review
Every user with privileged access needs a current business purpose. Remove dormant accounts and reduce excessive permissions, then replace shared logins with individual identities. Recovery email addresses and phone numbers belong to active, authorized people.
Creating a strong password requires sufficient length and a memorable construction. Verify unique credentials for the content system and registrar, with additional authentication for billing, connected email, analytics, and backup locations. Recovery codes need protected storage and named custody.
Extend the access review to integrations. Old API keys, webhook secrets, application passwords, and agency accounts may remain after a project ends. Revoking unnecessary credentials reduces the number of routes into the site and improves accountability.
Support and Service Terms
Examine support performance from the previous year. Outage and ticket records show response time and resolution quality, along with repeated causes and gaps in assistance. Give staff the contact methods and escalation path before an urgent event.
Read service limits alongside actual measurements. Storage and memory may have changed, as may processor time, database connections, worker limits, transfer allowances, backup retention, and staging access. Record pricing and renewal terms with any additional charges the business incurred.
When assessing reliable wordpress hosting, connect service features with operational requirements. Determine if current capacity and recovery tools match the site's role, then examine security controls, development access, and support procedures.
Ticket history can expose a mismatch that feature lists conceal. Repeated requests for the same database fault may indicate an unresolved application problem, while long delays before the first useful reply may point to an escalation gap. Compare the evidence from the busiest incident with the response described in the service terms. Note the first action that restored service and the information support required before taking it. This creates a practical basis for discussing renewal or changing internal procedures.
Written Decisions and Follow-Up
Separate urgent corrections from planned improvements in the final record. Each item needs a completion date and estimated cost, plus a named contact and verification method. Changes involving updates or migration need staging tests, a backup, and a rollback procedure.
Retain a compact evidence file with screenshots of resource use and exported performance results. Add restoration notes, an account inventory, support-ticket summaries, renewal dates, and the approved action list. Sensitive credentials do not belong in the report. Record their storage location and custodian without exposing the secret itself.
Comparing this file with the previous year's record shows the direction of change. Rising storage, slower peak responses, repeated security alerts, or longer restoration times can then be identified before they become an emergency. Record completed improvements so later reviewers do not repeat work or remove a control whose purpose is no longer obvious.
Use the same measurement definitions at the next review. A response-time figure taken from a different page or traffic period cannot show a reliable trend. Consistent measurements make the annual comparison useful without turning the review into continuous reporting.
Some checks belong on a shorter schedule. Critical updates, backup monitoring, availability alerts, account removal, and certificate renewal cannot wait for an annual meeting. The yearly review instead confirms that these recurring controls exist, have responsible owners, and produced evidence during the period.
An annual assessment turns gradual website change into a visible management decision. By recording business dependence, measured demand, tested recovery, security condition, access ownership, and support performance, a small business can correct emerging weaknesses before another year of growth makes them harder to resolve.

.jpg "How To Revolutionize Your E-commerce Business?")


